Seismic shift in Splunk pricing spotlights AI data management
The era of simply amassing heaps of raw telemetry is over, Splunk users say. Viable AI agents for automated IT ops will depend on putting all that data in context.
By
Beth Pariseau, Senior News Writer
Published: 18 Sep 2026
DENVER -- Splunk users stand to cut costs significantly with a recent pricing update, as raw telemetry collection gives way to the development of an advanced data architecture for AI.
Splunk rolled out activity-based pricing in controlled availability last month with its Machine Data Lake (MDL), a new bulk storage layer within the Cisco Data Fabric (CDF) framework for AI data management. Activity-based pricing balances between ingest-based pricing, which is based on the volume of data indexed per day, and workload-based pricing, which charges for resources used during search and analytics workflows. Both existing pricing models require users to index all data upon ingestion, which incurs charges in both cases; activity-based pricing doesn't require that step until data is searched.
The departure from universal indexing will have a major effect on how CIOs view Splunk, as AI data management becomes increasingly important to support autonomous agents, said Mike Leone, an analyst at Moor Insights & Strategy.
"The cost savings will be enough that I could see some customers completely reevaluating what they're indexing the traditional Splunk way," Leone said. "A lot of Splunk customers have spent years architecting around ingest-based licensing, deciding what to index versus what to keep somewhere cheaper. Weighting search equally with ingest changes that math."
Splunk: 'Add a zero' to data volumes at same cost
Splunk didn't disclose the specific cost of searches and indexing under activity-based pricing, but the goal is to let customers store orders of magnitude more data in MDL for the same price they paid previously, said Kamal Hathi, Splunk's senior vice president and general manager, in a keynote presentation at Splunk .conf26 this week.
Caption: Kamal Hathi, senior vice president and GM of Splunk, unveils new pricing at .conf 26.
"What you need in this agentic era is to grow your data maybe 10x, without having your bill go up in proportion," Hathi said. "What we want to do is allow you to add a zero to the amount of data that you're processing while keeping your cost the same."
Users can also use Federated Search to avoid indexing data until it's searched. Federated Search expanded this week to support Amazon CloudWatch and Databricks on AWS. Splunk officials also demonstrated a new Value Insights feature to help users assess which of Splunk's pricing options provide the most cost savings and said that an AI agent that optimizes storage tiering is in the works for CDF.
While Federated Search is of interest, MDL potentially allows more data to be stored closer at hand for quicker access during incidents, said Karun Subramanian, senior director of AI for infrastructure and operations at UnitedHealth Group, during a panel presentation at this week's conference.
"It's not just the access [to data]; it's the low-latency access, especially for agents in look-up analysis," Subramanian said. "You cannot really wait for an hour for data to be rehydrated [during an incident], and that is still a challenge with Federated Search."
[Users] are still worried about rising costs and indexing everything. MDL is the natural fix almost immediately.
Mike Leone, Analyst, Moor Insights & Strategy
Leone said MDL has the potential to have a much more immediate effect on AI cost control than the tokenomics tools Splunk also introduced this week for its Agent Observability product.
"They introduced so many different cost-saving techniques to a point where I could see customers getting a bit confused as to what would give them the biggest bang for their buck," he said. "A majority of the folks in the audience aren't there yet. They're still worried about rising costs and indexing everything. MDL is the natural fix almost immediately."
Data management can make or break AI automation
Multiple presenters at Splunk .conf26 emphasized the importance of well-organized data to provide context and direction to autonomous agents.
Constellation Energy, for example, uses AI features in Splunk's Agentic Security Operations Center (SOC) to counter mounting AI-driven attacks, according to a keynote presentation by Hossein Korsha, cybersecurity manager at the gas and electricity supplier headquartered in Baltimore. This AI-driven automation reduced the mean time to incident resolution for one application in Constellation's environment from 20 minutes to 39 seconds.
"[With AI], we're able to ingest and observe data much faster, which lets us create detections much faster, find out vulnerabilities much faster and overall speed up our entire SOC response," Korsha said.
Good data management has been integral to making AI automation work, he said. The company's earlier attempts to deploy Splunk's machine-learning-based Risk-Based Analytics (RBA) without well-curated data had an adverse effect.
"We adopted RBA without having a mature enough asset and identity framework in Splunk, and it resulted in analysts taking in a lot of false positives, and made us step back, review our work, and start from the ground [up]," Korsha said. "Once we actually got everything mature enough, then we started seeing amazing results. And things are just getting better as we make adjustments."
UnitedHealth's first attempt at building its own AI site reliability engineering (SRE) agent encountered similar issues due to fragmented data sources, Subramanian said during the panel presentation.
"[We started with] a low-level bolt-on integration, a lot of customization, not really pretty, but that was the only way we could do it," he said. "Different API calls to different systems to pull the right data as needed, and, of course, then used the power of LLMs to come up with root cause analysis. Accuracy-wise, we started at 10%-15% ... It's still not 80 or 90 that we would like it to be … but we're working on it."
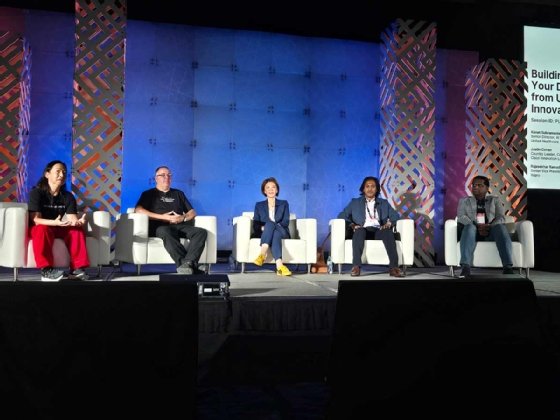
A Splunk .conf26 AI data management panel: (L-R) Sancha Norris, AI product marketing lead Splunk; Justin Cohen, leader, Cisco Innovation Labs Canada; Hanlin Fang, VP of products, Splunk; Karun Subramanian, senior director of AI, UnitedHealth; Rajasekhar Ramadas, global head of technology transformation, Wipro.
'From raw telemetry to AI-ready signals'
In a separate breakout presentation, Subramanian detailed the new data architecture required for an AI SRE agent to be most accurate -- one that contrasts with the existing method of simply amassing extensive stores of metrics, logs and traces for observability.
"AI is forcing us to rethink something much more fundamental than our tools. It's forcing us to rethink the data architecture," he said. "The shift that is required is going from raw telemetry to AI-ready signals."
Moving to AI-ready signals requires an additional context layer that combines systems telemetry with operational context from configuration management databases, IT service management tools, business metadata, source code and runbooks, Subramanian said. Another term for this is data fabric, and the Cisco Data Fabric "can really give you a shortcut to get to [that]," he said.
In addition to the MDL and Federated Search updates, Splunk shipped CDF components last month, including a data catalog and automation features for onboarding data into the Splunk Common Information Model format. A new Agent Launchpad no-code agent builder lets data analysts build agents that are triggered to take action in response to observability alerts.
Subramanian indicated during that session and the data management panel that he's interested in moving toward CDF, though he declined to answer follow-up questions from TechTarget News following his presentation to confirm.
In comments during the breakout presentation, Subramanian also cautioned that the CDF architecture is still new. "The context layer is up and coming," he said. "You won't find a lot of documentation around it … it's going to have a data catalog, knowledge graph and vector index, all to … get to the AI-ready signals stage."
Log data, Cisco network tie-ins bolster Splunk
Virtually every observability, data management and even data storage vendor is vying to become the data fabric of choice for IT buyers, and most offer something similar to the context layer Subramanian described.
But analysts say Splunk's long history of log management and analytics within big companies, combined with its integration of Cisco network topology, device health and event data into a new Network Intelligence App released this week, warrant serious consideration from IT buyers.
"Splunk has security data and operational data, and increasingly, network data -- that's a very unique data set," said Stephen Elliot, an analyst at IDC. "Add the new interface of Cisco Cloud Control, which is free with most Cisco purchases, and that enables [AI] context for various buyers -- that's a very interesting approach to meeting different roles where they are."
Beth Pariseau, senior news writer for Informa TechTarget, is an award-winning veteran of IT journalism. Have a tip? Email her or connect on LinkedIn.