Cyberattacks that disrupted refrigeration systems across hundreds of French supermarkets highlight the growing risks posed by exposed operational technology (OT). As connected devices proliferate, organizations must rethink how they secure the systems controlling physical processes.
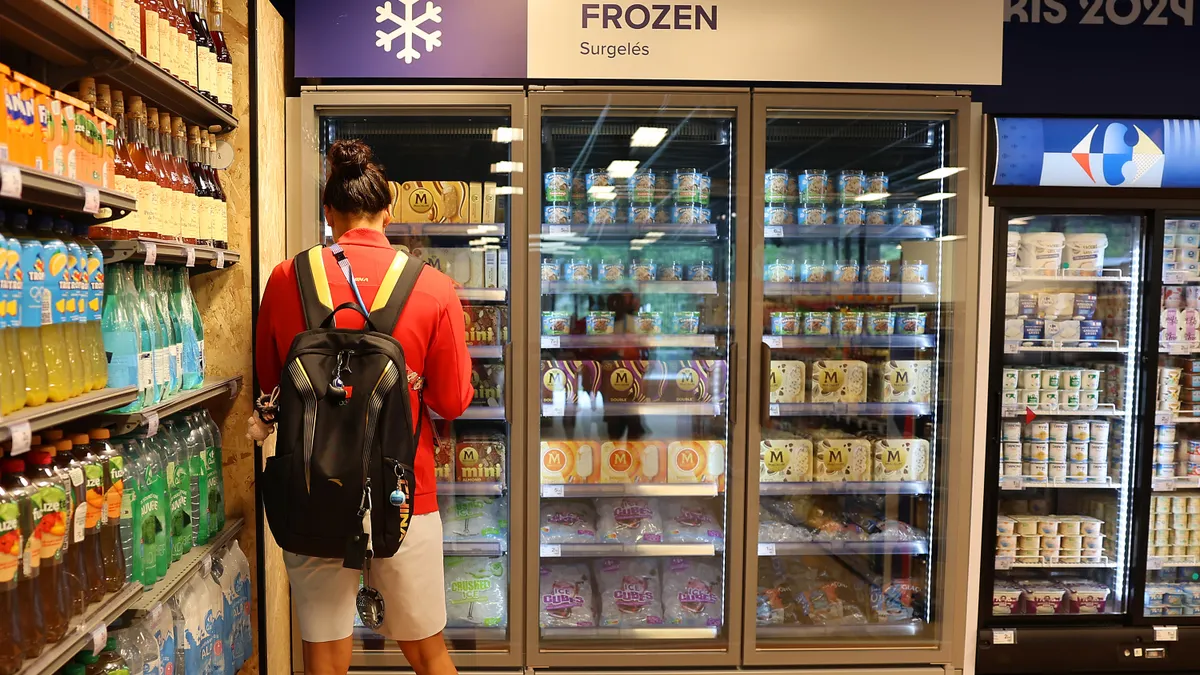
The initial incident, which caused cooling units to overheat in hundreds of French supermarkets in October, demonstrated how cyberthreats can translate into physical consequences. By hijacking the software governing the refrigeration controls, threat actors drove temperatures up overnight — spoiling vast amounts of inventory, triggering fires and inflicting millions of euros in damage.
The issue came to the fore again this week, as news emerged that supermarket chains across at least seven additional European countries — including Belgium, Ireland and Sweden — suffered similar overnight outages, raising fridge and freezer temperatures as high as 50°C (122°F) and sparking warnings from EU officials about deliberate supply chain disruption.
While the escalating incidents attracted attention due to severe stock losses, the underlying problem is familiar to security researchers: OT remains an often-overlooked and inadequately guarded attack surface.
Experts emphasize that the core significance lies in what these incidents reveal about the wider security of connected infrastructure. The issue is not simply that refrigeration systems are tied to external networks, but that critical devices controlling physical processes are increasingly accessible from the public internet without adequate security controls.
The physical blast radius of exposed OT
OT systems monitor and control physical environments across manufacturing, utilities, healthcare and commercial facilities. When compromised, they can affect equipment, inventory, safety and essential operations, extending the consequences beyond stolen data or disrupted IT services.
While food retail is the latest target, OT attacks have impacted multiple critical sectors. Similar exposures have repeatedly surfaced across municipal water treatment plants, power distribution networks, and commercial HVAC building controls where remote management capabilities were introduced without adequate perimeter protections.
At the heart of the issue is a fundamental architectural oversight: the failure to distinguish between a connected device and an exposed one. A controller sending data to a properly secured monitoring platform is not equivalent to one whose management interface is directly accessible from the public internet.
However, reflexively disconnecting these devices altogether is not necessarily the answer. Modern enterprise operations rely heavily on connectivity for predictive maintenance, automated environmental monitoring and the early identification of equipment failures. The imperative is to secure the remote access that businesses increasingly depend on, rather than assume that removing connectivity is a practical solution.
Legacy systems and fragmented responsibility
Third-party access represents one of the most critical security gaps in modern OT environments. Equipment contractors and refrigeration specialists often require remote access to maintain systems, leaving enterprise IT teams with zero visibility into how those external connections are configured or authenticated.
Experts warn that the European supermarket hacks should be viewed as a warning rather than an isolated event.
Daniel dos Santos, head of security research at Forescout’s Vedere Labs, says the rapid expansion of connected endpoints is outpacing defensive controls.
“It’s the old adage that cybersecurity is a team sport: everybody has to play together,” dos Santos said. “So, at the end of the day, it is still a sort of soft underbelly.”
Andrew Tierney, head of hardware at Pen Test Partners, believes the security of IoT devices has improved, but remains more concerned about industrial control systems, where longstanding weaknesses persist.
“My bigger worry these days is the industrial control systems space, where it's not technically IoT — it’s hardware — but we’re still seeing the same mistakes being made today that we’ve seen being made 10 years ago,” he said.
He added that many products remain insecure, despite the growing need to connect equipment for monitoring, data collection and automation. Industrial systems that once had minimal external connectivity are increasingly exposed to similar risks.
Exposing the attack surface
The European refrigeration incidents demonstrate how trivial weaknesses in connected equipment can move beyond the digital environment and cause real-world disruption.
Older devices may also retain default credentials or run outdated software, while publicly accessible information can help attackers identify potential targets.
Tierney notes that specialized search engines like Shodan remain useful for finding internet-exposed devices, although its coverage of IP addresses and ports has become less comprehensive. Other discovery platforms similarly offer defenders broader visibility into exposed software and hardware configurations.
Even relatively simple changes, such as moving a service away from its default port, can make a device less likely to appear in Shodan’s results. However, this should not be mistaken for a security measure: changing a port does not prevent a determined attacker from discovering an exposed service.
The broader concern is that a weakness repeated across multiple installations can turn an individual vulnerability into a widespread liability. Where similar equipment and configurations are deployed across hundreds of sites, attackers may be able to exploit the same weakness repeatedly.
A wake-up call for the industry
The immediate lesson from the European freezer incidents is that organizations need a clearer understanding of their OT environments, including which devices are connected, who is responsible for them and how they can be accessed. Cybersecurity must be treated as an operational risk, rather than solely an IT concern.
That starts with maintaining an exhaustive inventory of connected devices, mapping internal dependencies, and ensuring controllers are never exposed directly to the public internet without robust authentication and segmentation. Where remote management is essential, access should be restricted through secure mechanisms, supported by strong authentication and appropriate network controls.
Responsibility must also extend across the entire vendor ecosystem. Suppliers and third-party contractors must be held to strict security baselines, while customers need sufficient visibility to assess the risks.
The next incident may not involve supermarket freezers. It could affect building controls, manufacturing equipment, water infrastructure or healthcare systems. Devices responsible for storing temperature-sensitive medicines, for example, could have serious consequences if their environmental controls were compromised.
The lesson is not that connected infrastructure should be abandoned, but that connectivity must be accompanied by security, visibility and accountability. As attackers gain more opportunities to target physical processes, treating OT as a secondary concern is an increasingly difficult risk to justify.